
Publisher Network Onboarding: Automated Site Quality Auditing, MFA Detection, and Policy Compliance
Under Google Ad Manager (GAM) Multiple Customer Management (MCM) governance rules, a single non-compliant child publisher serving ad requests on
Under Google Ad Manager (GAM) Multiple Customer Management (MCM) governance rules, a single non-compliant child publisher serving ad requests on policy-violating pages or Made-for-Advertising (MFA) layouts can trigger network-wide ad serving restrictions, clawbacks on finalized earnings, and termination of parent Manage Inventory (MI) or Manage Account (MA) delegations. For a sell-side platform managing thousands of web, mobile application, and Connected TV (CTV) supply sources, relying on manual spreadsheet reviews during initial domain vetting creates an unacceptable operational vulnerability. Human reviewers examining a static homepage URL cannot reliably inspect asynchronous JavaScript execution, dynamic slot injection, viewport-relative ad stacking, or paid traffic arbitrage funnels operating exclusively on deep subdirectory landing pages.
Protecting institutional demand partnerships and maintaining reliable Net-30 and Net-60 payment cycles for legitimate publishers requires shifting compliance verification from periodic manual audits to deterministic, automated pre-onboarding telemetry. Modern tier-1 DSPs actively score SSP supply paths based on bid density, viewability verification, invalid traffic (IVT) rates, and content categorization. When an SSP permits low-quality or policy-violating child domains into its auction stream, buying algorithms respond with aggressive QPS throttling and supply path optimization (SPO) penalties that depress clearing prices across the entire exchange.
At Sky Boosts, our publisher onboarding architecture functions as an automated engineering gatekeeper before a child network receives an MCM invitation, a Prebid.js 11.x wrapper configuration, or a Prebid Server endpoint. By combining headless Chromium DOM instrumentation, cryptographic supply chain validation, and continuous post-onboarding bid stream inspection partnered with HUMAN and Pixalate pre-bid filtration, we enforce a 100% Google-compliant, mainstream brand-safe environment with zero tolerance for alcohol, gambling, adult, tobacco, or restricted categories.
Defining Made-for-Advertising (MFA) Inventory Under ANA and IAB Guidelines
The programmatic industry's focus on Made-for-Advertising inventory crystallized following the Association of National Advertisers (ANA) programmatic media supply chain transparency investigations and subsequent technical frameworks established by the IAB Tech Lab. While no single HTTP header declares a property as MFA, these domains share an unmistakable engineering and economic blueprint: they exist solely to capture programmatic working media through arbitrage, offering minimal editorial utility while maximizing impression volume per user session.
Under ANA and IAB evaluation models, MFA classification is not triggered by a solitary metric, but rather by the convergence of five operational vectors:
- Excessive ad-to-content viewport density that crowds out editorial text or video player real estate.
- Aggressive, non-viewable, or sub-threshold auto-refresh timers designed to inflate bid request volume per session.
- Heavy reliance on paid traffic acquisition funnels sourced from social networks and native content recommendation widgets.
- High-latency, template-driven site architectures engineered for forced pagination, such as multi-page slideshows where each click triggers a full wrapper reload.
- Disconnected supply paths where inventory is resold across numerous unauthorized
ads.txtreseller lines to obscure the domain's true performance metrics.
For an SSP or parent MCM network, allowing MFA properties into the open exchange or curated deal IDs corrupts historical auction data. Even when MFA slots register high technical viewability due to sticky viewport pinning, they deliver near-zero post-click conversion utility for advertisers. Consequently, tier-1 DSPs deploy machine learning classifiers that ingest domain-level telemetry to automatically bid-shade or block suspected MFA supply paths. Enforcing strict brand-safety and MFA filtering at the network ingestion layer prevents this toxic supply from diluting auction clearing prices for premium publishers.
Ad-to-Content Ratio Thresholds and Auto-Refresh Abuse
Quantifying ad congestion requires evaluating rendered pixel geometry across standardized desktop (1920x1080) and mobile (390x844) viewports rather than merely counting <script> tags in the raw HTML source. Modern programmatic wrappers instantiate slots dynamically as the user scrolls. A compliant publisher layout maintains an in-viewport ad-to-content ratio strictly below 30%, meaning the cumulative surface area of all visible advertisement containers at any scroll depth never exceeds 30% of the active browser viewport area (window.innerWidth * window.innerHeight).
MFA operators routinely breach this threshold by combining sticky header banners, persistent footer anchors, twin skyscraper rails, and interstitial outstream video players that collectively consume 50% to 75% of the screen. Furthermore, when measured across the entire document height (document.documentElement.scrollHeight), compliant properties demonstrate a clear majority of semantic editorial nodes (<article>, <p>, <main>) relative to ad slot bounding boxes. If cumulative vertical ad height exceeds total rendered editorial text height, the page fails basic quality auditing.
Equally destructive to supply path health is predatory auto-refresh engineering. In Prebid.js 11.x and Google Publisher Tag (GPT) integrations, refreshing ad slots is only compliant when governed by strict viewability and duration gates:
- Minimum Interval Enforcement: Refreshes must never execute faster than every 30 to 60 seconds, and only while the specific slot maintains continuous IAB Active View eligibility (at least 50% of pixels in the viewport for 1 continuous second for display, or 2 seconds for video) verified via the browser's
IntersectionObserverAPI. - User Activity Verification: Compliant refresh controllers listen for active DOM engagement events (
scroll,keydown,pointermove, or page visibility statedocument.visibilityState === 'visible') and pause timers immediately when the browser tab loses focus. - OpenRTB 2.6 Transparency: Every refreshed impression must accurately declare its state in the outgoing OpenRTB 2.6 bid request via the
imp.ext.refreshobject, specifying both the refresh count (count) and the trigger intervals (refsettings).
MFA sites bypass these rules by executing blind setInterval() loops every 10 to 15 seconds, calling pbjs.requestBids() and googletag.pubads().refresh() regardless of whether the ad container is in the active viewport or whether the user has abandoned the tab. DSPs track impression depth per user session and penalize endpoints that omit refresh metadata or flood the bid stream with high-frequency, low-attention refresh requests.
Paid Traffic Arbitrage Signatures in Referrer Headers
Because MFA domains possess virtually zero organic brand equity or direct navigation bookmarks, their traffic survival depends entirely on paid visitor acquisition. Arbitrage operators purchase low-cost clicks from social platforms or native content discovery widgets using sensationalized headlines, funneling users onto landing pages packed with high-density programmatic display and instream/outstream VAST 4.3 video units. As long as the Revenue Per Session (RPS) generated through programmatic auctions exceeds the Cost Per Click (CPC) paid to acquire the visitor, the operator scales the campaign.
Detecting arbitrage funnels requires deep inspection of HTTP Referer headers, client-side document.referrer strings, and URL query parameter structures at both the pre-onboarding crawler stage and the real-time edge collector. Arbitrage traffic leaves clear forensic signatures in the request pipeline:
- Query String Entropy and Click Trackers: Arbitrage landing URLs frequently append dense tracking arrays containing
utm_source,utm_medium=paid,utm_campaign, platform-specific click identifiers (fbclid,gclid,ttclid), and proprietary arbitrage sub-IDs used to reconcile real-time yield per creative headline. - Referrer Distribution Skew: Legitimate editorial publishers exhibit a balanced traffic distribution across direct navigation, organic search engines, syndication feeds, and organic social referrals. When more than 60% of a domain's incoming bid requests carry referrer headers originating from paid social redirects or native ad widget domains, the site is flagged for arbitrage scrutiny.
- Subdirectory Isolation: Sophisticated operators host a clean, editorial-looking homepage at the root domain (
example.com) to pass manual network reviews, while routing 99% of paid arbitrage traffic to isolated subdirectories (example.com/trending/story-id-9482?page=1) that feature radically different ad unit density and aggressive floor pricing.
By correlating URL path entropy with referrer distributions, our ingestion engine isolates domains that weaponize dynamic routing to hide arbitrage templates from standard root-domain audits.
Building an Automated Pre-Onboarding Crawler for Child Publishers
To eliminate manual vetting blind spots, Sky Boosts executes a multi-stage automated crawling pipeline before any child publisher domain is approved within our unified monetization platform. Built on a distributed cluster of headless Chromium instances orchestrated via Playwright, the auditing engine emulates real desktop and mobile device profiles routed through both residential and carrier-grade proxy networks. This architecture prevents deceptive publishers from serving stripped-down HTML to known datacenter IP ranges or standard bot user agents.
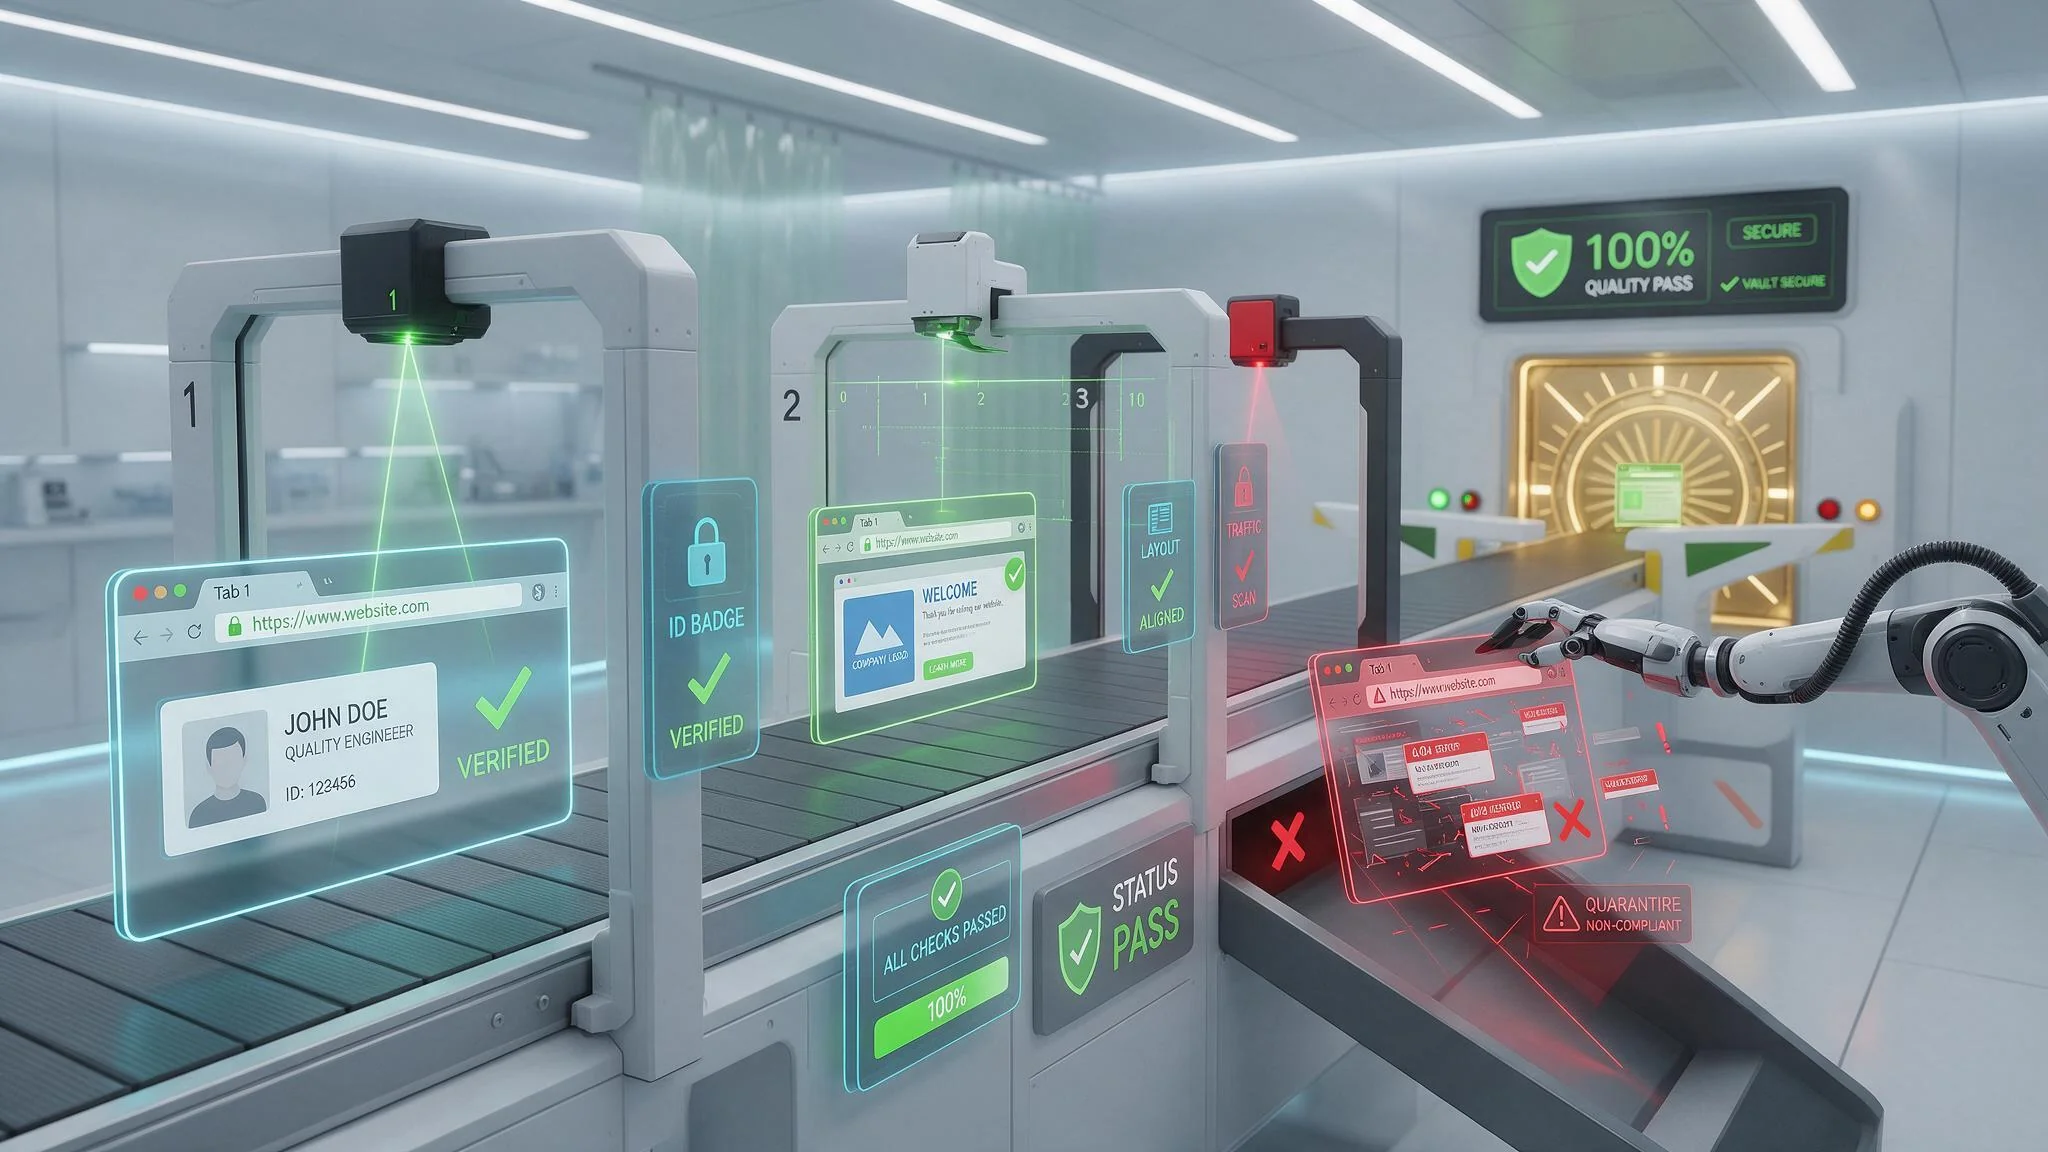
When a prospective publisher submits a domain for onboarding, the crawler does not merely fetch the root URL. Instead, it constructs a representative site graph by parsing sitemap.xml, traversing internal navigation links, and sampling deep article paths. Across each sampled URL, the headless browser intercepts all outgoing network calls, inspects TLS certificate chains, parses supply chain authorization files, and executes runtime JavaScript assertions against the live DOM after waiting for asynchronous ad scripts and lazy-loaded components to settle.
Verifying ads.txt v1.1 Authorization and Domain Age
Before evaluating page layout, the onboarding pipeline verifies cryptographic and administrative domain ownership alongside IAB Tech Lab ads.txt v1.1 (and app-ads.txt for mobile and CTV bundles) compliance. Inventory spoofing and unauthorized reselling remain persistent vectors for ad fraud, and parent MCM networks must ensure that prospective publishers maintain clean, transparent supply paths.
Our crawler fetches https://{domain}/ads.txt over strict HTTPS, validating HTTP 200 status codes and text/plain MIME types to ensure the file is not returning a soft-404 HTML redirect. The parser enforces ads.txt v1.1 specifications:
- Manager and Owner Directives: The parser extracts
OWNERDOMAINandMANAGERDOMAINvariables to verify that the legal business entity applying for monetization matches the declared owner of the web property and corresponds cleanly to the parent SSP'ssellers.jsonentries. - File Bloating and Reseller Ratios: Legitimate publishers maintain concise
ads.txtfiles listing their direct monetization partners (DIRECT) and a curated set of authorized resellers (RESELLER). If a prospective domain presents anads.txtfile containing thousands of indiscriminateRESELLERlines copied from public aggregator lists, it indicates poor supply path hygiene or participation in unauthorized arbitrage pools. - RDAP and DNS Telemetry: Concurrently, the pipeline queries Registration Data Access Protocol (RDAP) and historical DNS records. Domains registered within the preceding 90 days, domains exhibiting rapid nameserver churn, or recently expired domains repurposed with AI-generated scraped content are automatically rejected before reaching human review.
DOM Inspection for Screens Without Publisher Content and Stacked Slots
Once domain provenance is established, the Playwright cluster evaluates content compliance and slot geometry. Google Publisher Policies strictly prohibit serving Google ads on screens without publisher content, with low-value content, under construction, or where user attention is expected to be elsewhere. In practice, policy enforcement strikes frequently occur when publishers inject global header or footer ad wrappers that inadvertently render on utility screens, such as login portals, password reset forms, empty search results, 404 error pages, or interstitial exit gates.
To audit both content volume and geometric ad compliance programmatically, our headless Chromium worker injects a diagnostic script into the page context after network idle (networkidle) and scroll simulation. The following production script illustrates how the crawler measures semantic text density, computes the exact viewport ad-to-content ratio, and detects illegal slot stacking (where multiple ad containers overlap in 2D space via absolute or fixed CSS positioning):
// Executed inside Playwright page.evaluate() after simulated scroll and GPT/Prebid load
async function auditPageQualityAndAdGeometry() {
  const vw = window.innerWidth;
  const vh = window.innerHeight;
  const viewportArea = vw * vh;

  // 1. Evaluate Semantic Editorial Content to detect "Screens Without Publisher Content"
  const contentSelectors = 'article, main, [role="main"], .post-content, p';
  const textNodes = Array.from(document.querySelectorAll(contentSelectors));
  const cleanText = textNodes
    .map(el => el.innerText.trim())
    .join(' ')
    .replace(/\s+/g, ' ');
  const wordCount = cleanText.length > 0 ? cleanText.split(' ').length : 0;

  // 2. Collect Active Ad Containers (GPT Slots, Prebid Wrappers, and Iframes)
  const adElements = new Set();
  if (window.googletag && typeof window.googletag.pubads === 'function') {
    window.googletag.pubads().getSlots().forEach(slot => {
      const el = document.getElementById(slot.getSlotElementId());
      if (el) adElements.add(el);
    });
  }
  document.querySelectorAll('[id^="div-gpt-ad"], [data-ad-unit], iframe[id^="google_ads_iframe"]').forEach(el => {
    adElements.add(el);
  });

  // 3. Calculate Viewport Ad Density and Detect Overlapping/Stacked Slots
  const boxes = [];
  let visibleAdArea = 0;
  let hiddenSlotViolations = 0;

  adElements.forEach(el => {
    const style = window.getComputedStyle(el);
    const rect = el.getBoundingClientRect();

    // Flag 1x1 pixel stuffing or opacity cloaking
    if (parseFloat(style.opacity) < 0.1 || style.visibility === 'hidden' || (rect.width === 1 && rect.height === 1)) {
      hiddenSlotViolations++;
      return;
    }

    if (rect.width > 0 && rect.height > 0) {
      boxes.push({ id: el.id || 'anon-slot', rect });

      // Calculate intersection with current active viewport
      const xOverlap = Math.max(0, Math.min(rect.right, vw) - Math.max(rect.left, 0));
      const yOverlap = Math.max(0, Math.min(rect.bottom, vh) - Math.max(rect.top, 0));
      visibleAdArea += (xOverlap * yOverlap);
    }
  });

  // Check pairwise geometric intersection for stacked ads
  let stackedSlotPairs = 0;
  for (let i = 0; i < boxes.length; i++) {
    for (let j = i + 1; j < boxes.length; j++) {
      const a = boxes[i].rect;
      const b = boxes[j].rect;
      const intersectX = Math.max(0, Math.min(a.right, b.right) - Math.max(a.left, b.left));
      const intersectY = Math.max(0, Math.min(a.bottom, b.bottom) - Math.max(a.top, b.top));
      if (intersectX * intersectY > 100) { // Threshold > 100 sq px to ignore minor border overlap
        stackedSlotPairs++;
      }
    }
  }

  const adToViewportRatio = Number((visibleAdArea / viewportArea).toFixed(4));

  return {
    wordCount,
    totalAdSlotsDetected: boxes.length,
    adToViewportRatio,
    stackedSlotPairs,
    hiddenSlotViolations,
    isCompliant: wordCount >= 250 && adToViewportRatio <= 0.30 && stackedSlotPairs === 0 && hiddenSlotViolations === 0
  };
}
If any sampled URL returns wordCount < 250 while instantiating active ad slots, the crawler flags the template for violating the "screens without publisher content" rule. Similarly, any instance where stackedSlotPairs > 0 or hiddenSlotViolations > 0 triggers an immediate hard rejection for ad stacking or pixel stuffing. Furthermore, the text corpus extracted during step 1 is passed through a lexical classifier that blocks domains containing prohibited verticals: alcohol, gambling, adult content, tobacco, firearms, or unverified medical claims.
Continuous Post-Onboarding Monitoring to Protect Parent MCM Standing
Passing pre-onboarding auditing is a mandatory prerequisite, but static point-in-time approval cannot defend an SSP against post-onboarding configuration drift or deliberate bait-and-switch tactics. Bad actors frequently submit a clean, low-density editorial site to secure GAM MCM approval and Prebid Server credentials, wait until the first billing cycle stabilizes, and then deploy high-frequency auto-refresh wrappers or paid arbitrage subdirectories during weekend traffic windows.
To protect our parent MCM standing and preserve auction integrity for our publishers, Sky Boosts runs continuous, real-time post-onboarding surveillance across three synchronized telemetry streams:
- Real-Time OpenRTB 2.6 Bid Stream Anomaly Detection: Our Prebid Server (Go/Java) and edge ingestion clusters log streaming telemetry across
site.page,site.ref,imp.ext.refresh, and device IP distributions. If a child publisher's sudden QPS spike correlates with newly introduced URL query strings or an abnormal surge inimp.ext.refresh.countvalues, an automated rate-limiter throttles outbound bid requests for that specific domain within 60 seconds. - Pre-Bid IVT Filtration with HUMAN and Pixalate: Every incoming impression opportunity across Web, Mobile App, and CTV (including OpenRTB 2.6 video and VAST 4.3 SSAI/CSAI endpoints) is scored in real time against HUMAN and Pixalate invalid traffic models. If a child domain's General Invalid Traffic (GIVT) or Sophisticated Invalid Traffic (SIVT) rate breaches strict internal basis-point tolerances, the offending supply is severed at the edge before reaching DSP bidding pipes.
- Automated GAM Policy Center Synchronization: Through scheduled polling of the Google Ad Manager API and Policy Center webhook alerts, our compliance engine monitors page-level enforcement actions across every linked MCM child account. If a publisher inadvertently serves ad tags on an under-construction subdirectory or triggers a low-value content warning, our platform automatically injects a URL-level blocklist rule into the edge wrapper configuration, suppressing ad rendering on the offending paths while alerting the publisher's engineering team.
When AdOps and platform engineering teams enforce deterministic, code-driven compliance at every stage of the supply lifecycle, every participant in the value chain benefits. DSPs gain high-converting, MFA-free inventory with verified viewability; the parent SSP eliminates policy clawback exposure; and legitimate publishers enjoy premium CPM clearing prices backed by predictable, institutional Net-30 and Net-60 payouts. Treating site quality auditing as a continuous systems engineering problem rather than an administrative checklist is the foundation of sustainable programmatic yield.